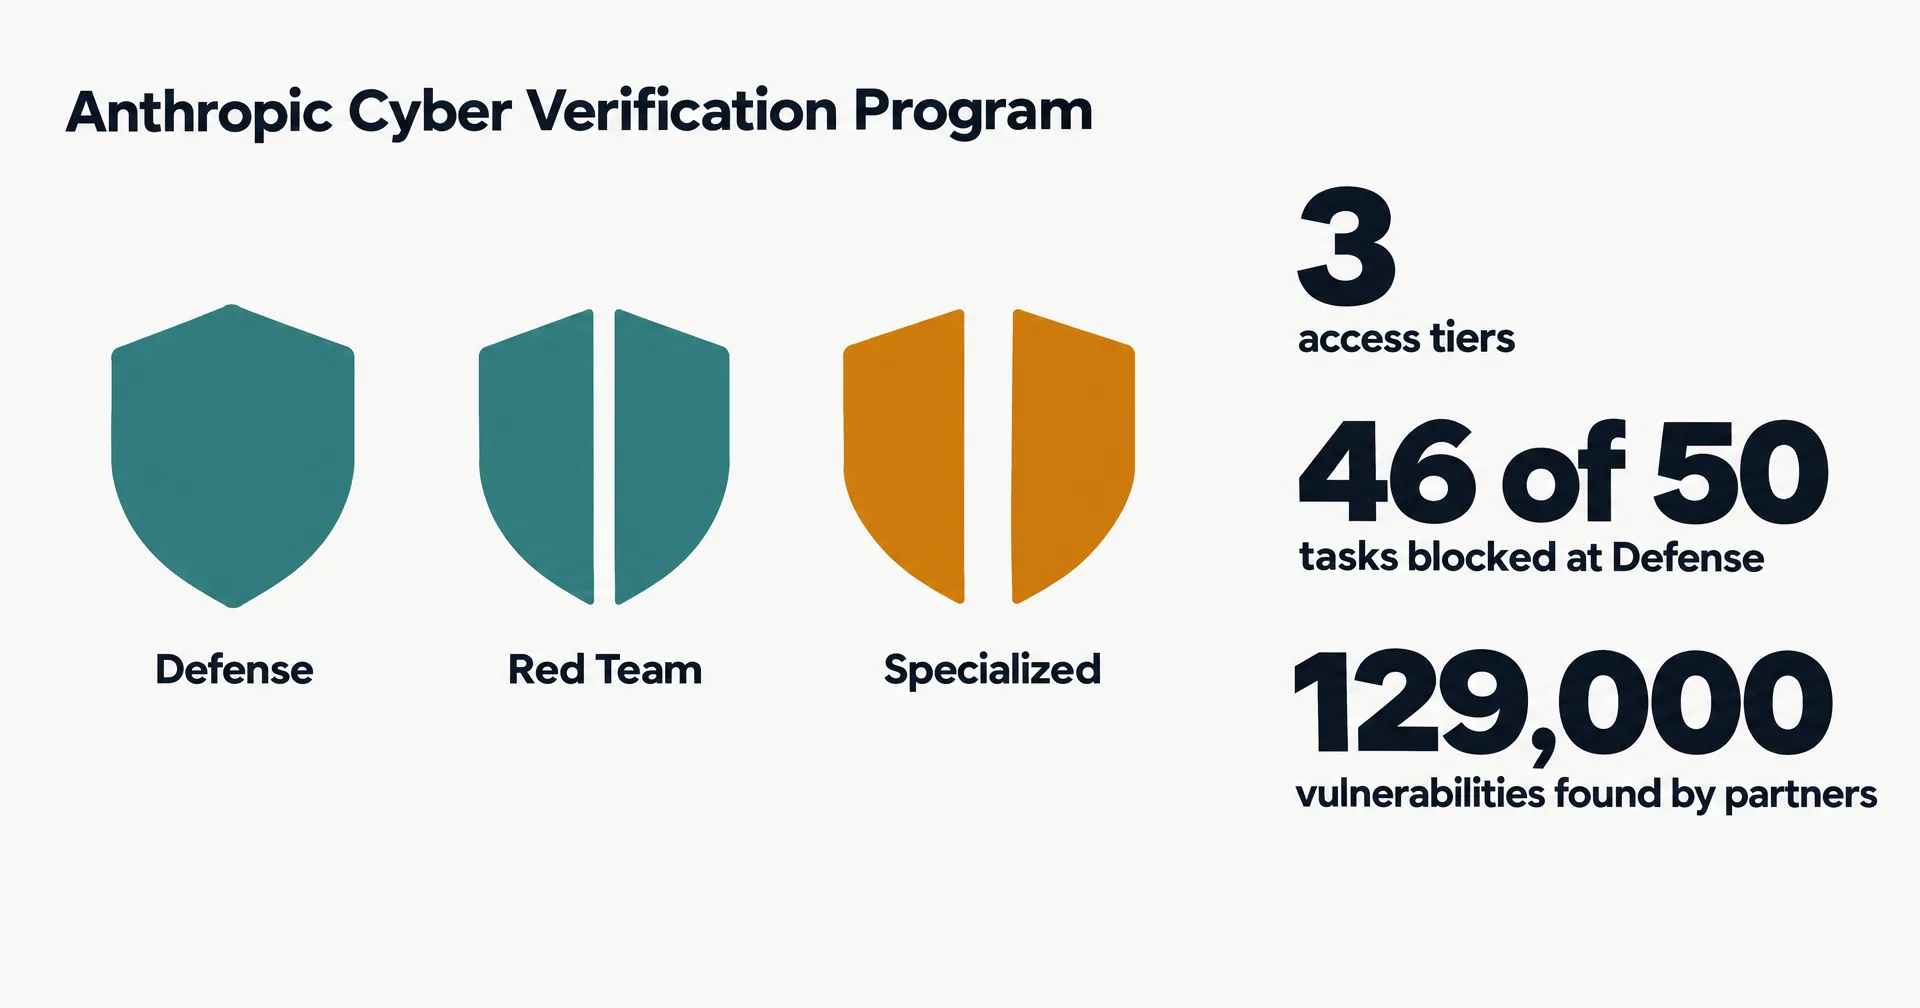
Anthropic expanded its Cyber Verification Program on October 6, 2026 into three access tiers, Defense, Red Team and Specialized, that give vetted security teams Claude models with fewer cyber blocks. The program now folds in Project Glasswing, the invite-only access to Claude Mythos, and covers Claude Opus 5.5, Claude Sonnet 5.5 and Claude Mythos 5.1. The reason it exists: Anthropic’s generally available models “have conservative cyber safeguards that block most cyber work.” On Anthropic’s own test, Claude Opus 5.5 completed 34 of 50 offensive scenarios in the Red Team tier, while without the program every one was blocked on the first prompt. This page reads Anthropic’s announcement and its Help Center article on cyber safeguards, as of October 6, 2026.
On this page · 7 sectionsOpen
 Anthropic expanded its Cyber Verification Program on October 6, 2026 into three access tiers, Defense, Red Team and Specialized, folding in Project Glasswing, its invite-only Claude Mythos program.
 Defense Access covers security operations, incident response, malware reverse engineering and vulnerability validation; Anthropic aims to answer applications within a few days.
 Red Team Access adds authorized penetration testing for organizations only, takes a few weeks to review, and still blocks ransomware and attacks on physical systems.
 Specialized Access, with the fewest blocks, is for testing systems such as power grids and flight systems, reviewed with the US government; Glasswing members move here.
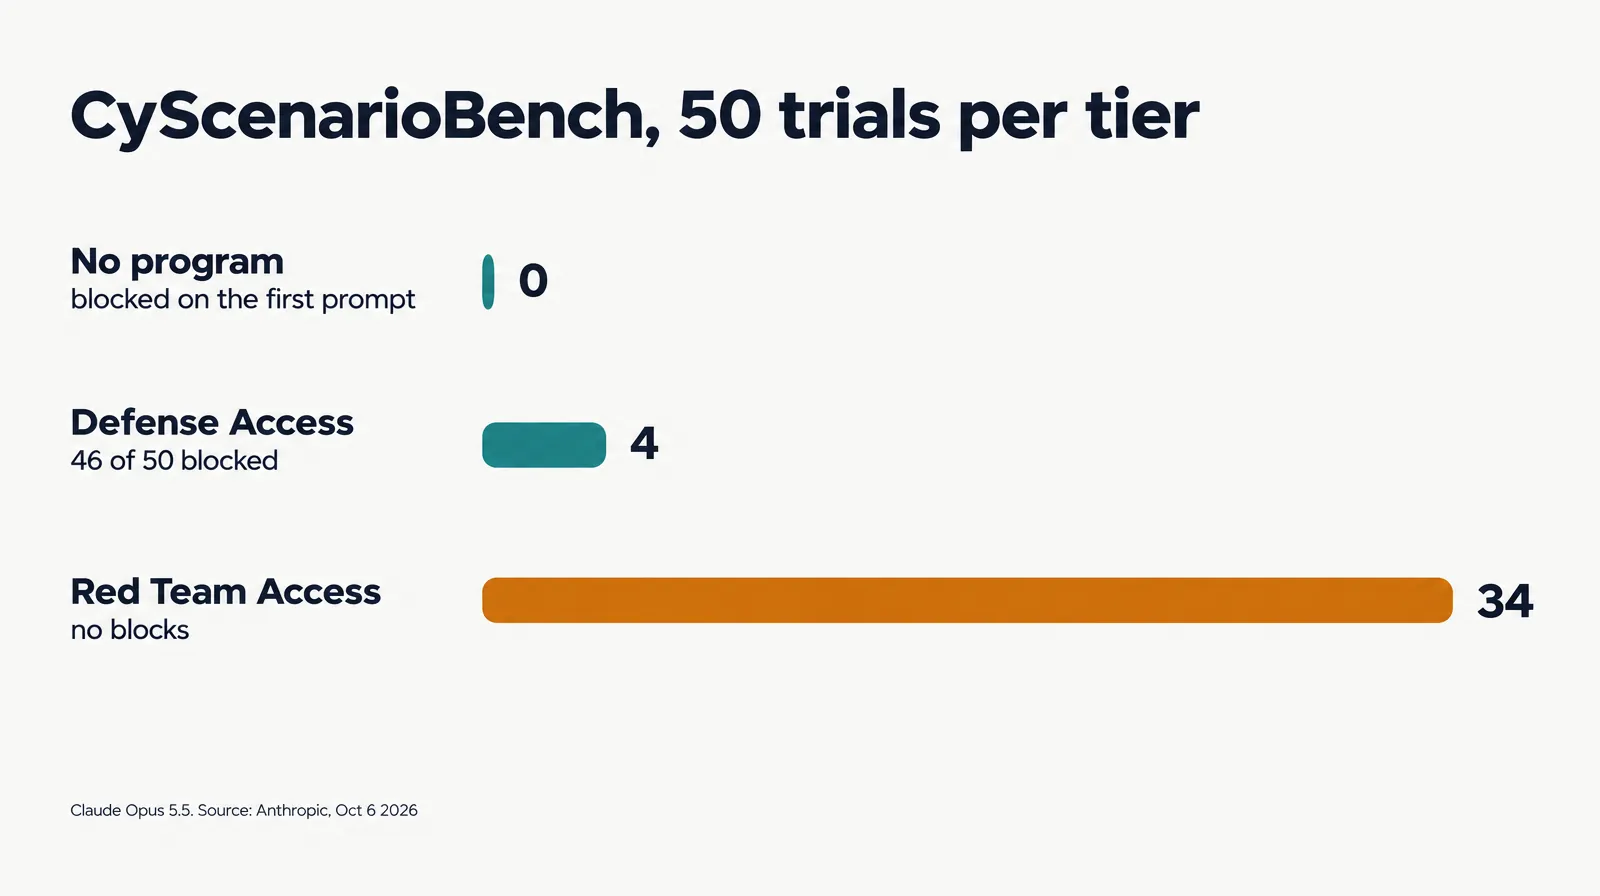
 On Anthropic’s CyScenarioBench, Claude Opus 5.5 completed 0 of 50 tasks without the program, 4 in Defense Access and 34 in Red Team Access, matching its unsafeguarded rate.
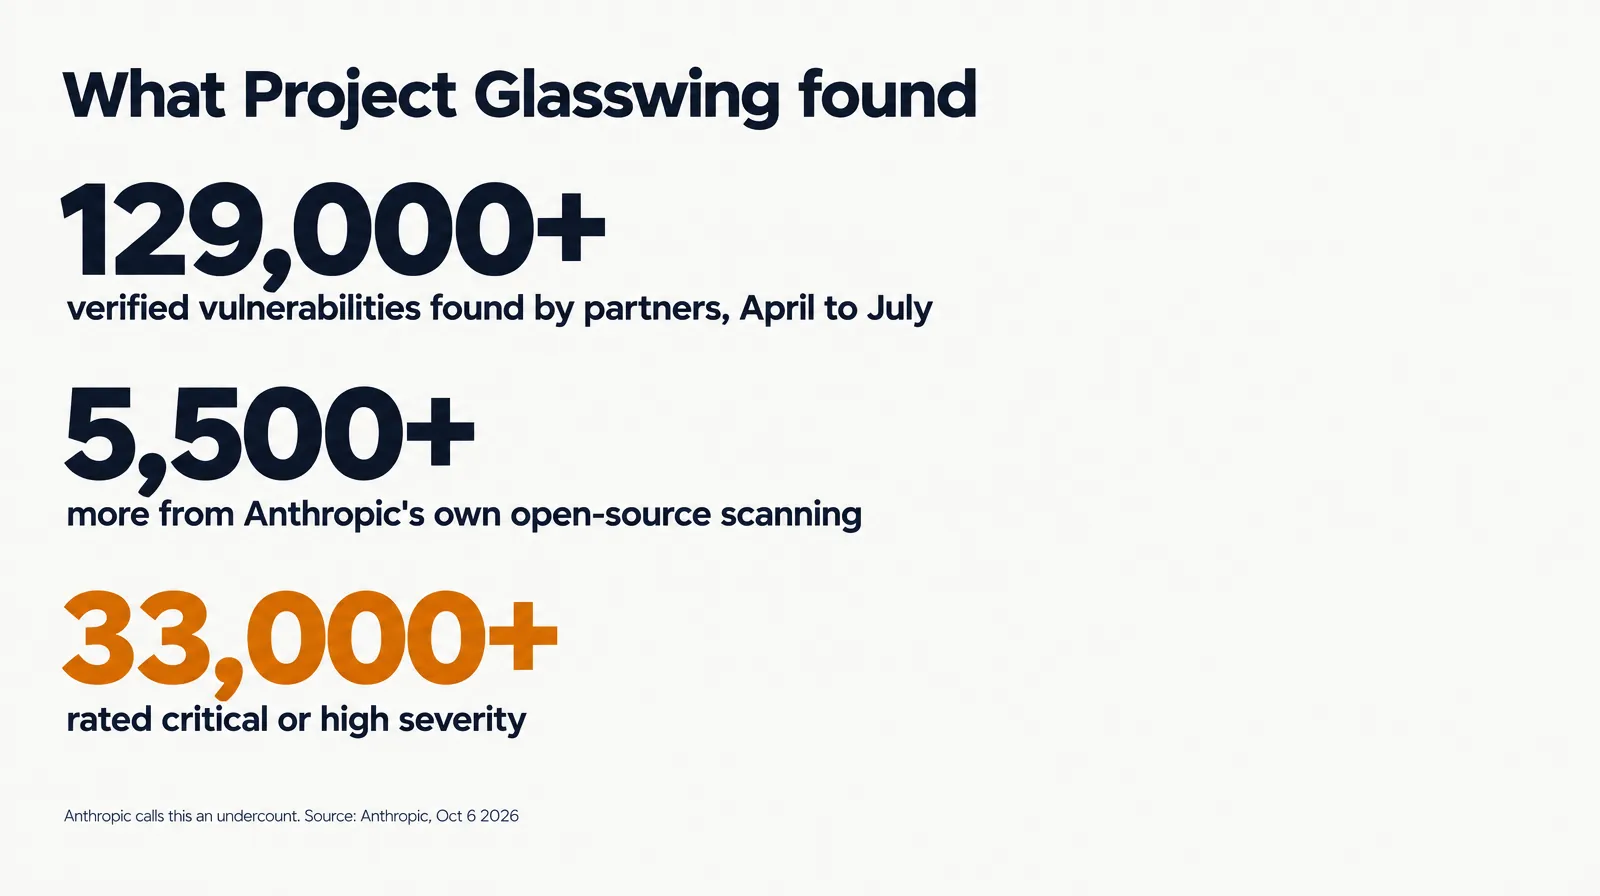
 Glasswing partners found at least 129,000 verified vulnerabilities from April to July 2026, more than 33,000 of them critical or high severity, which Anthropic calls an undercount.
§ 01The three tiers
| Tier | What it allows | Who qualifies | Review time |
|---|---|---|---|
| Defense Access | Security operations and incident response, malware reverse engineering, analyzing and validating vulnerabilities | Security teams at companies, nonprofits, universities and government; critical infrastructure operators of any size; smaller security firms; open-source maintainers; individual researchers with a record of reported vulnerabilities | Within a few days |
| Red Team Access | Everything above plus authorized penetration testing and red teaming | In-house and government red teams, security and penetration testing firms; organizations only | A few weeks; applicants get Defense Access while they wait |
| Specialized Access | The fewest cyber blocks, for testing safety systems such as flight systems, power grids, telecom networks and interbank transfers | A limited set of verified organizations, reviewed with the US government; Project Glasswing members move here | In-depth review |
Even Red Team Access keeps real-time blocks on “actions that could cause physical harm or mass disruption, such as deploying ransomware, damaging physical systems, or pen testing high-risk safety systems.” Every enrolled organization must allow data retention so Anthropic can watch for misuse; a zero-retention option, Enterprise Frontier Safeguards, is due later this fall, per Anthropic. Anthropic is explicit that its standard models still handle “code review, patching known issues, vulnerability finding in owned source code, and triage of security alerts” without any program.
§ 02What the tiers block, on Anthropic’s own test
Anthropic ran Claude Opus 5.5 through CyScenarioBench, its evaluation of multi-stage cyber operations, five attempts at each of 10 challenges per tier.
| Setting | Blocked | Completed, of 50 |
|---|---|---|
| No program | Every task, on the first prompt | 0 |
| Defense Access | 46 of 50 trials, at some point | 4 |
| Red Team Access | None | 34 |
| No safeguards (stands in for Specialized) | None | 67.6% success rate |
The tiers behave as designed on this test: Defense blocks offensive scenarios, Red Team removes the blocks, and 34 of 50 is the same completion rate Anthropic measured with no safeguards at all. It is Anthropic’s own benchmark, run by Anthropic.
§ 03What Project Glasswing found
Glasswing was the invite-only program that gave a group of organizations securing critical software access to Claude Mythos. Anthropic published its first numbers with this announcement.
| Figure | Number |
|---|---|
| Verified vulnerabilities found by partners, April to July 2026 | At least 129,000 |
| Found by Anthropic’s own open-source scanning, April to October 2026 | 5,500 more |
| Rated critical or high severity | More than 33,000 |
| Partner reports behind the figures | 33 |
Anthropic calls these “likely an undercount” based on a subset of partners and says it expects the true impact “to be at least five times higher”. Fewer than half of partners disclosed how many issues they had patched, so no patch rate is given.
§ 04Where it runs and how to apply
The program is available on the Claude Platform, Google Cloud’s Vertex AI and Microsoft Foundry; on Amazon Bedrock only for customers eligible for Enterprise Frontier Safeguards. Organizations apply through Anthropic’s CVP portal, prove the security controls each tier requires, and admins assign access per workspace. Existing members keep their settings and are evaluated for the new models automatically.
§ 05What this means if you run agents
For most teams nothing changes: the standard models still review code, patch known issues and triage alerts. The program matters for security teams whose work looks offensive to a classifier, such as malware analysis or authorized penetration tests. It also shows where frontier labs are heading: the most capable models arrive with use-based access tiers, verified identities and retained logs, not a single open API.
§ 06The record
As of October 6, 2026, 19:10 UTC: Anthropic’s announcement carries a publish time of 19:00 UTC. Every figure here is Anthropic’s, from that post; CyScenarioBench is Anthropic’s own evaluation.
§ 07Sources
- Anthropic, Expanding the Cyber Verification Program, October 6, 2026; read 19:09 UTC.
- Anthropic Help Center, Real-time cyber safeguards on Claude Opus and Sonnet.
- Anthropic, Project Glasswing and Enterprise Frontier Safeguards.
- Our records: Anthropic’s GLM-5.3 cyber report; Anthropic’s September threat report.
Q1What is Anthropic's Cyber Verification Program?
A program that gives vetted security professionals Claude models with fewer cyber blocks. Since October 6, 2026 it has three tiers, Defense, Red Team and Specialized, and it absorbed Project Glasswing, the invite-only access to Claude Mythos.
Q2Why do security teams need it?
Anthropic says its generally available models, including Claude Opus 5.5, Fable 5.1 and Sonnet 5.5, have conservative cyber safeguards that block most cyber work. The program lifts some of those blocks for verified defenders.
Q3How long does approval take?
Anthropic aims to answer Defense Access applications within a few days. Red Team Access takes a few weeks, and applicants get Defense Access while they wait. Specialized Access is reviewed in depth with the US government.
Q4Does Red Team Access remove every block?
No. Anthropic says users still hit real-time blocks on actions that could cause physical harm or mass disruption, such as deploying ransomware or testing high-risk safety systems. On its CyScenarioBench test, Red Team Access completed 34 of 50 tasks.
Q5Where is the program available?
On the Claude Platform, Google Cloud’s Vertex AI and Microsoft Foundry. On Amazon Bedrock it is available only to customers eligible for Enterprise Frontier Safeguards, due later this fall.